Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
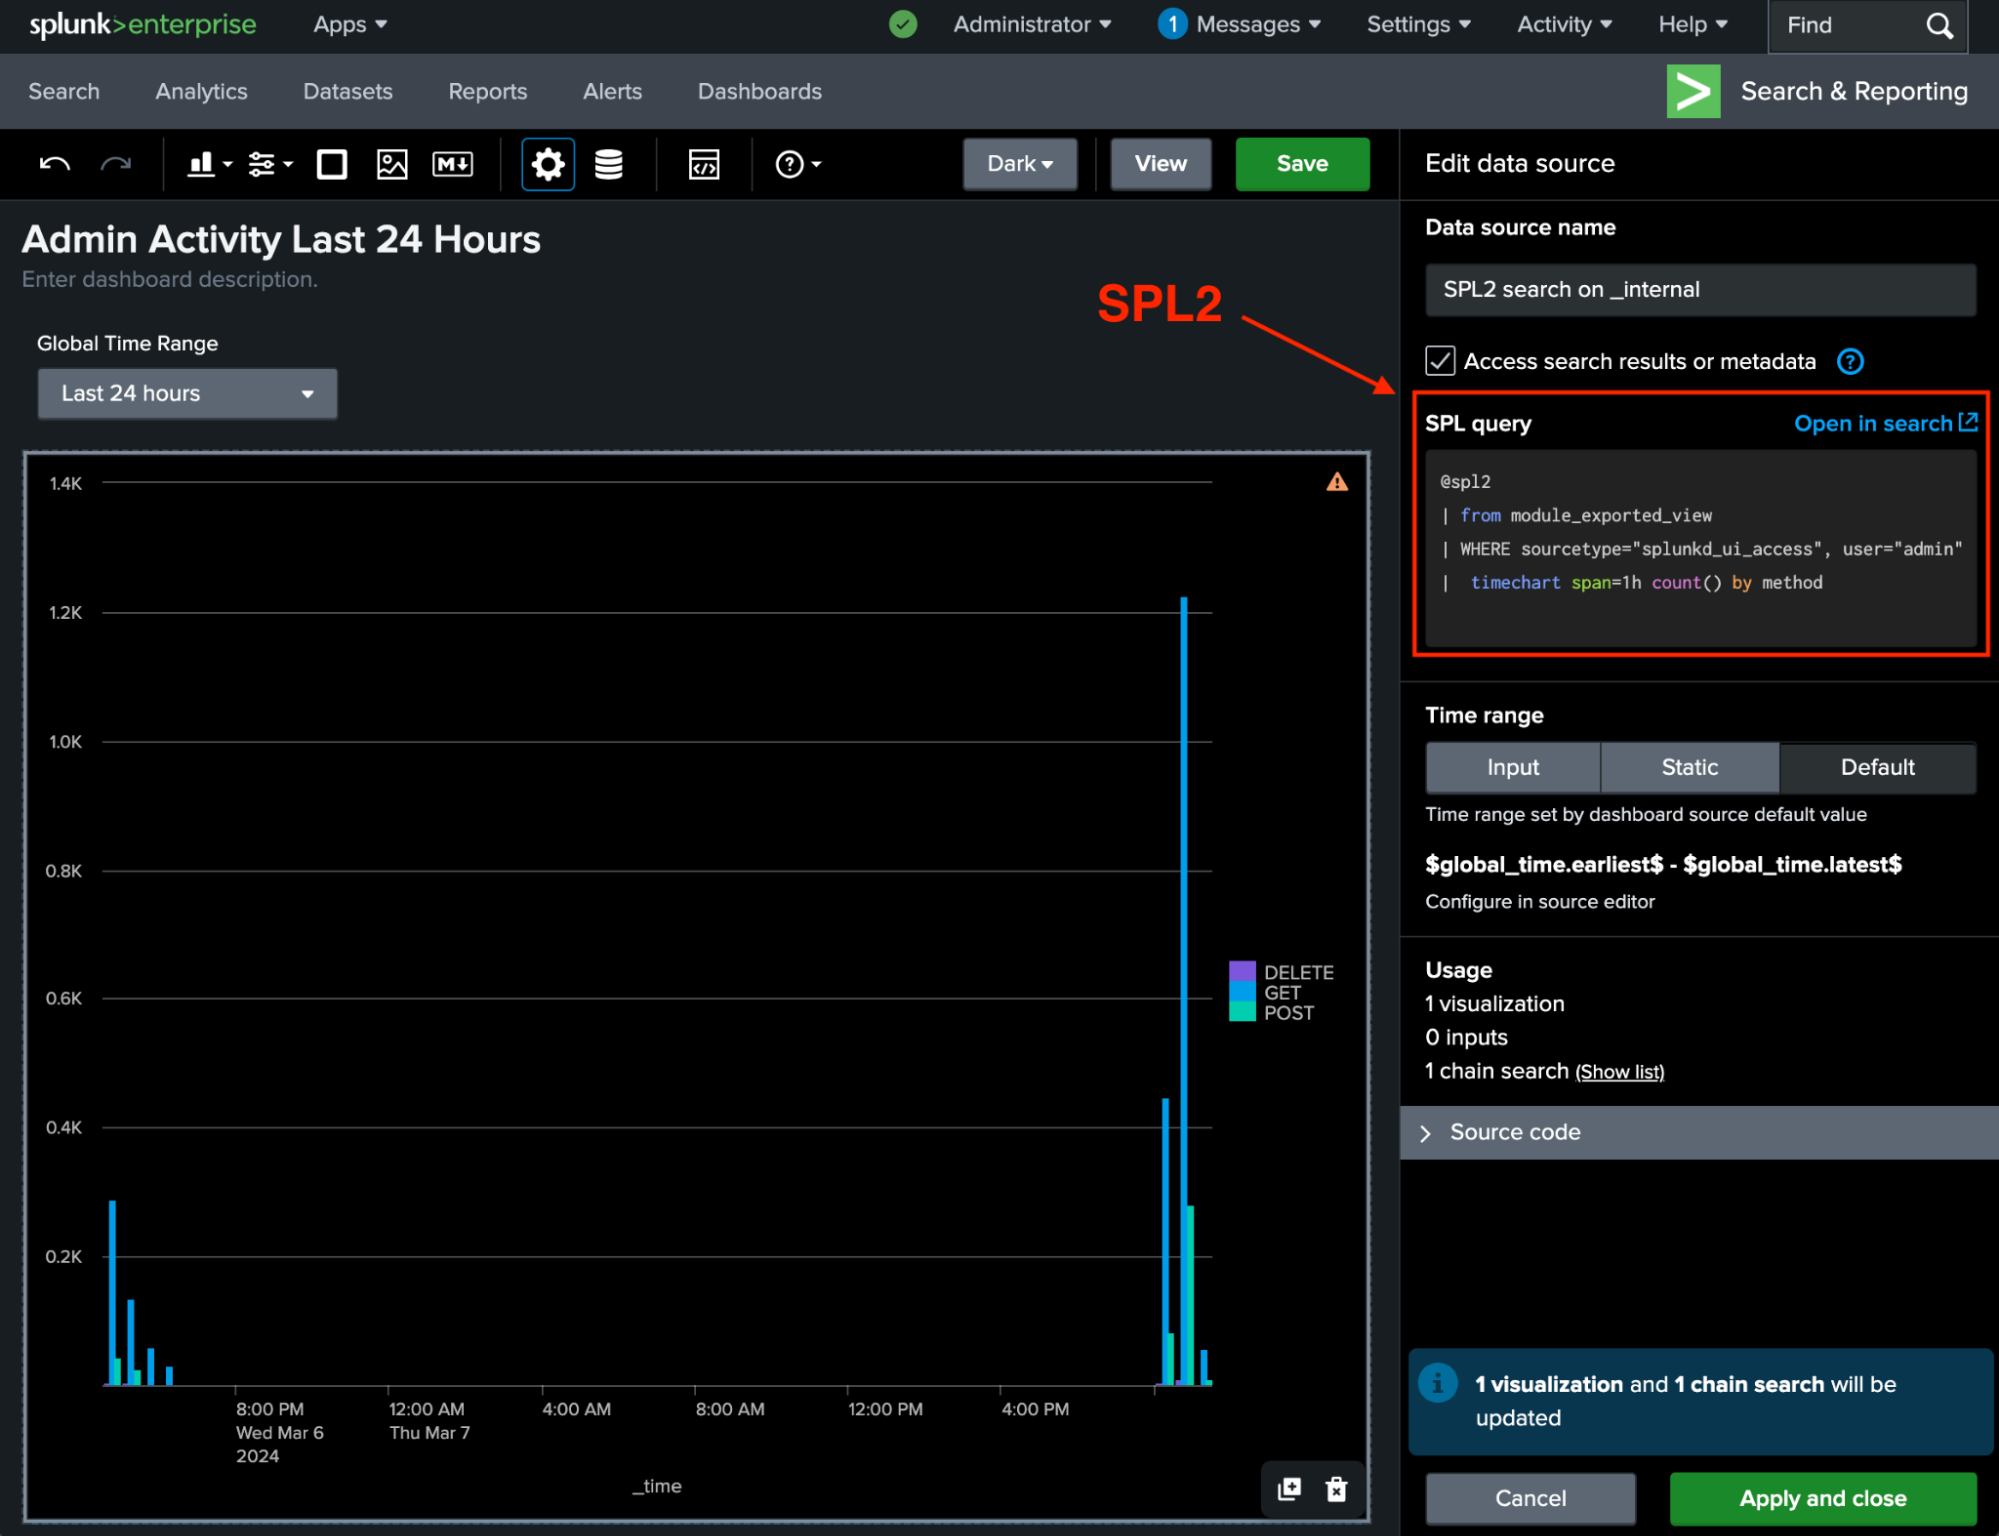
Announcing the Public Beta of SPL2 in Splunk Enterprise | Splunk
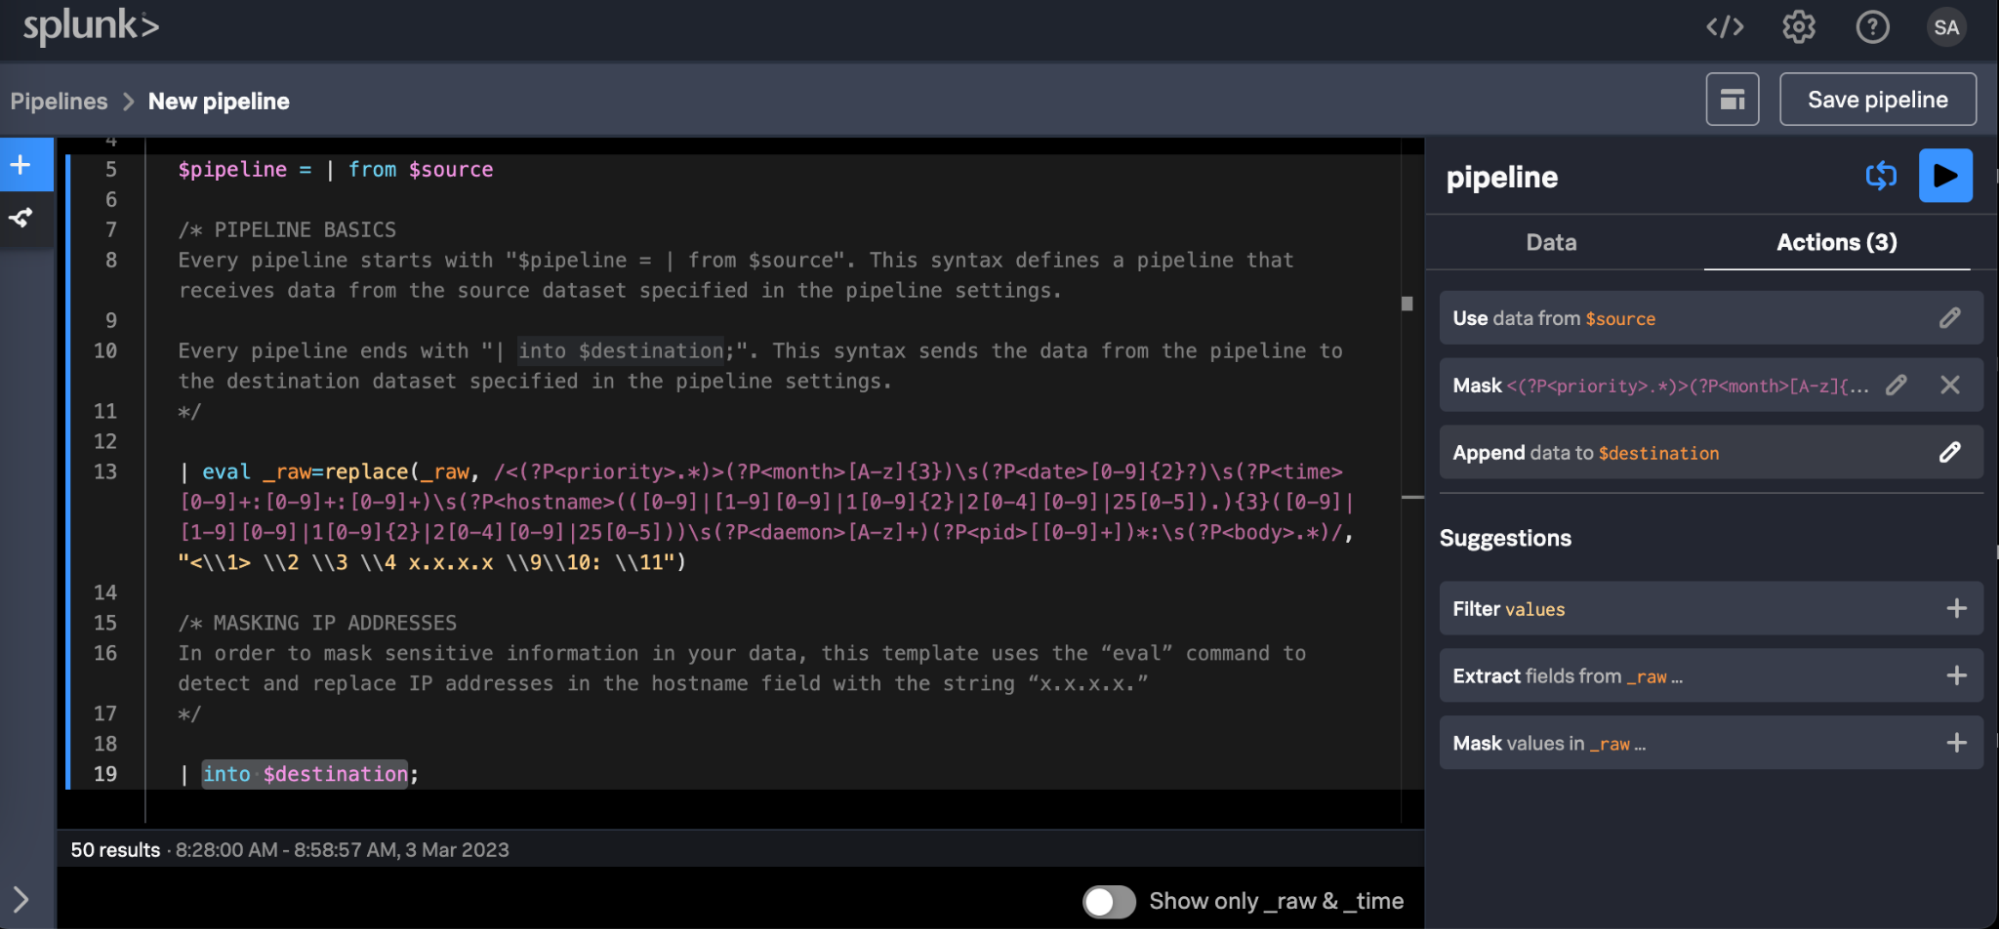
Announcing the Splunk SPL to SPL2 Converter | Splunk
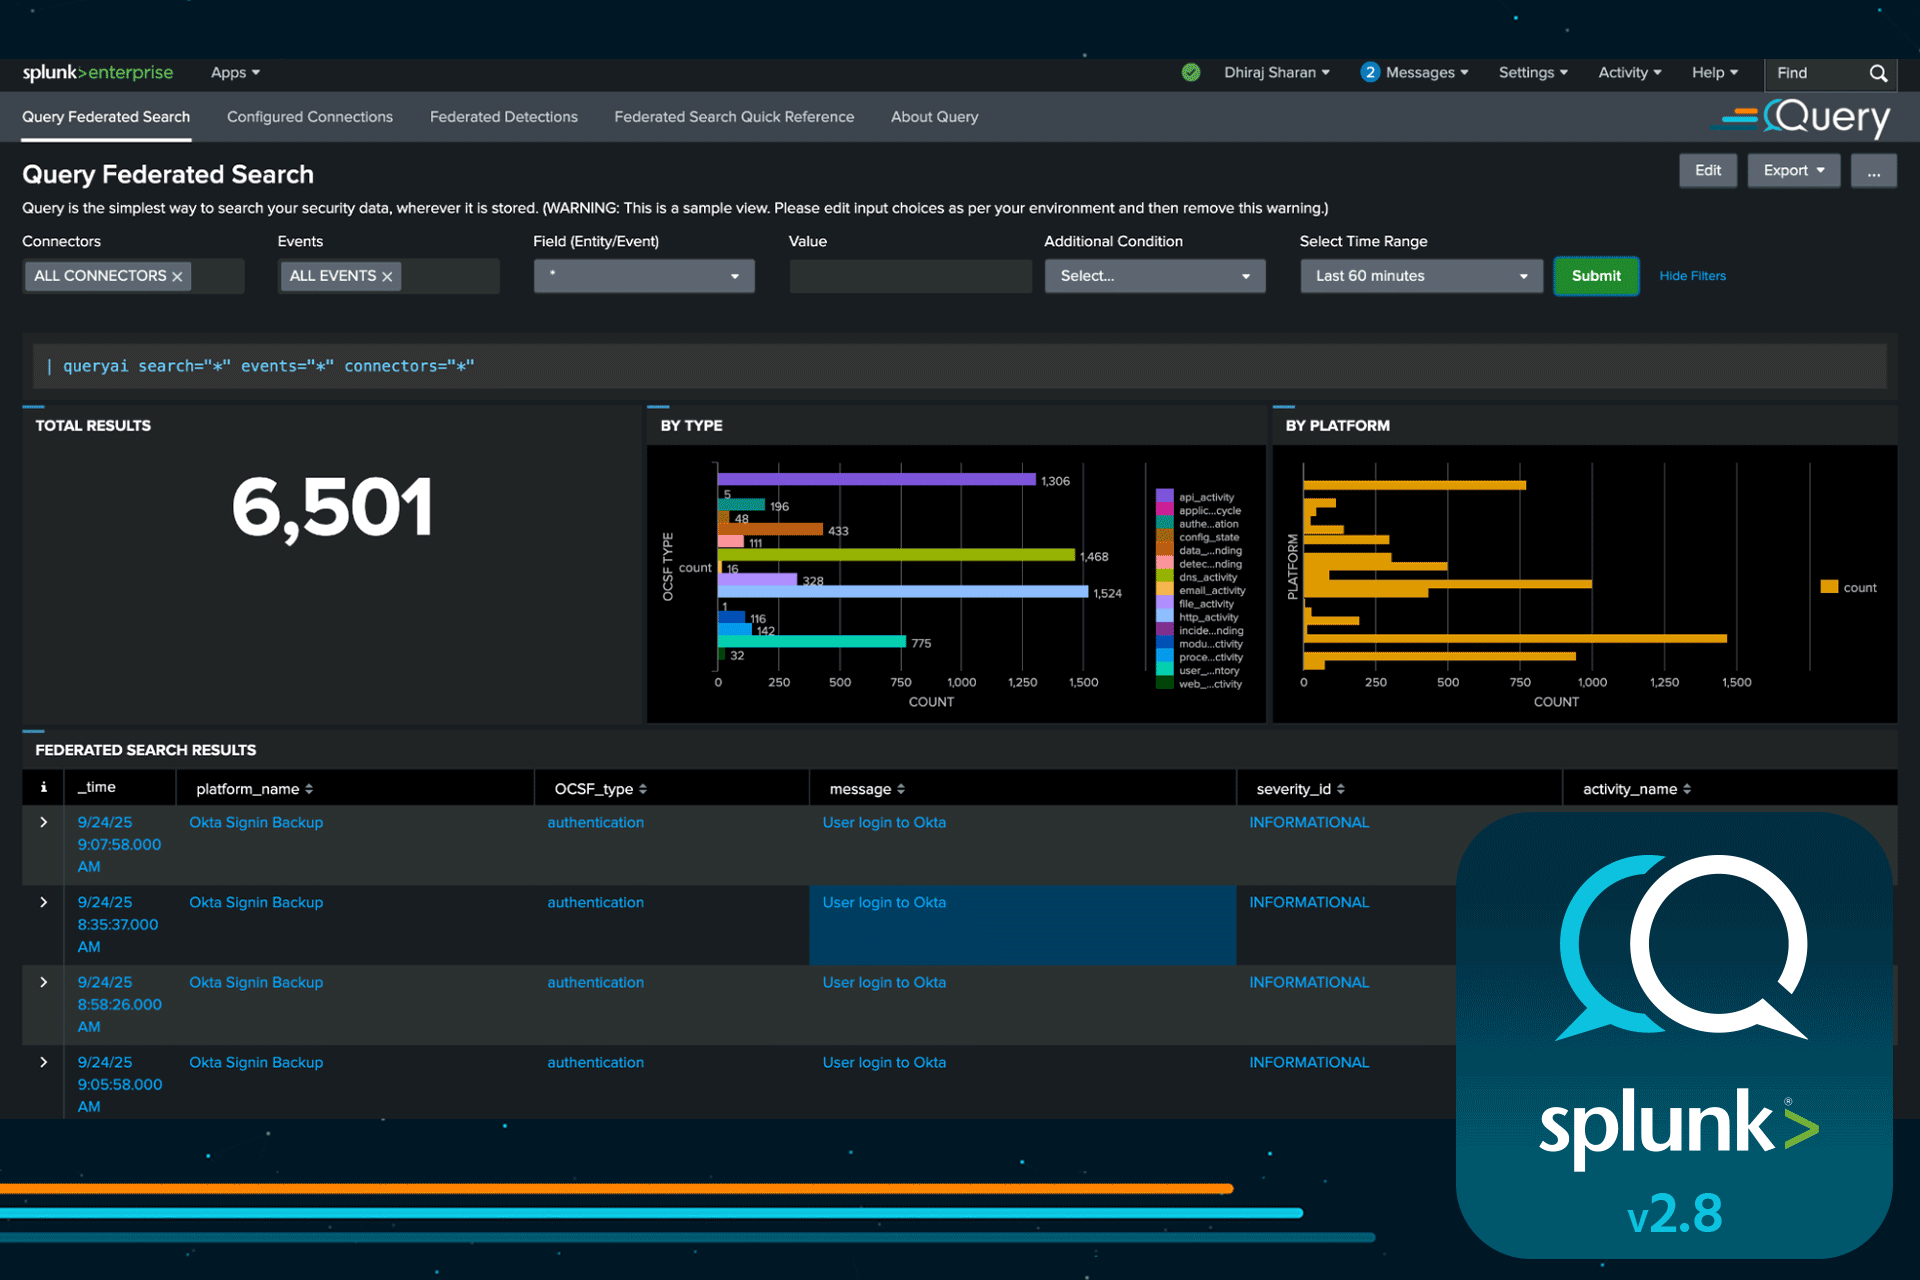
Product Release: Announcing Query Splunk App 2.8 - Query
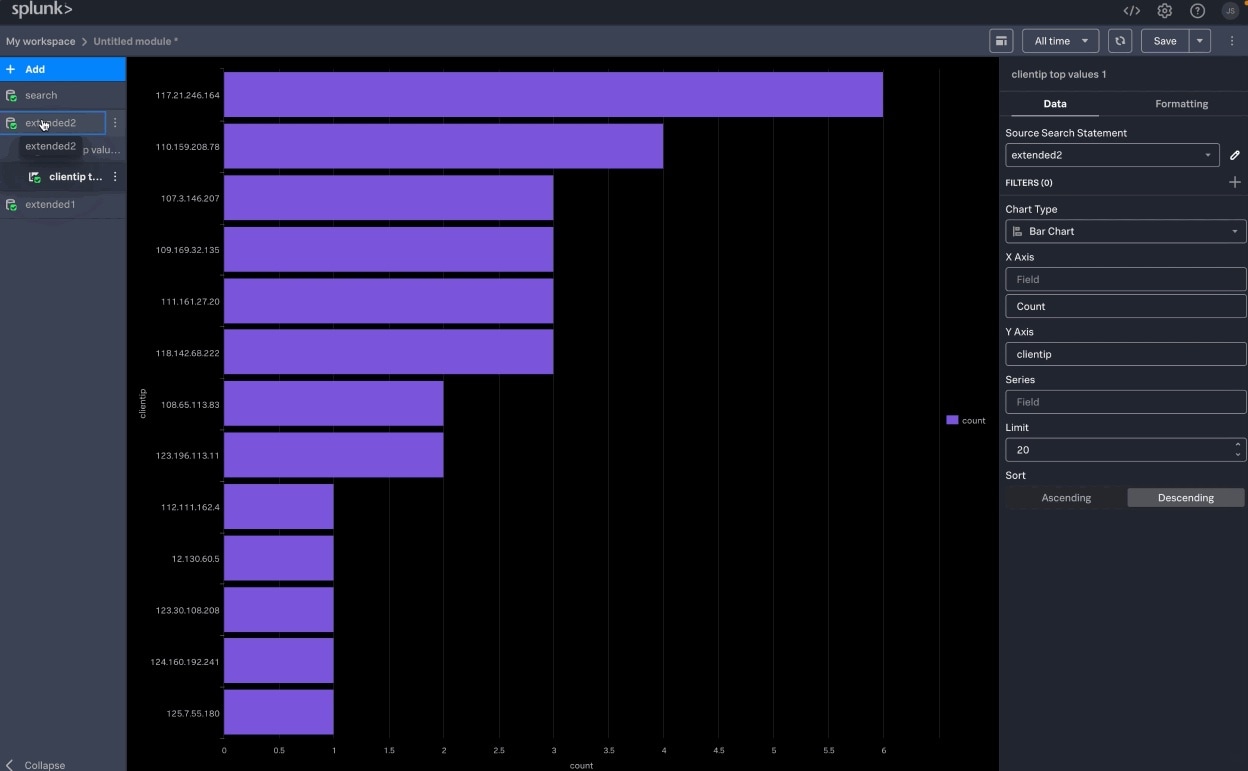
Discover how SPL2 enhances data querying in Splunk with improved syntax ...
Searching data using SPL2 | Splunk Enterprise, Splunk Cloud Platform ...
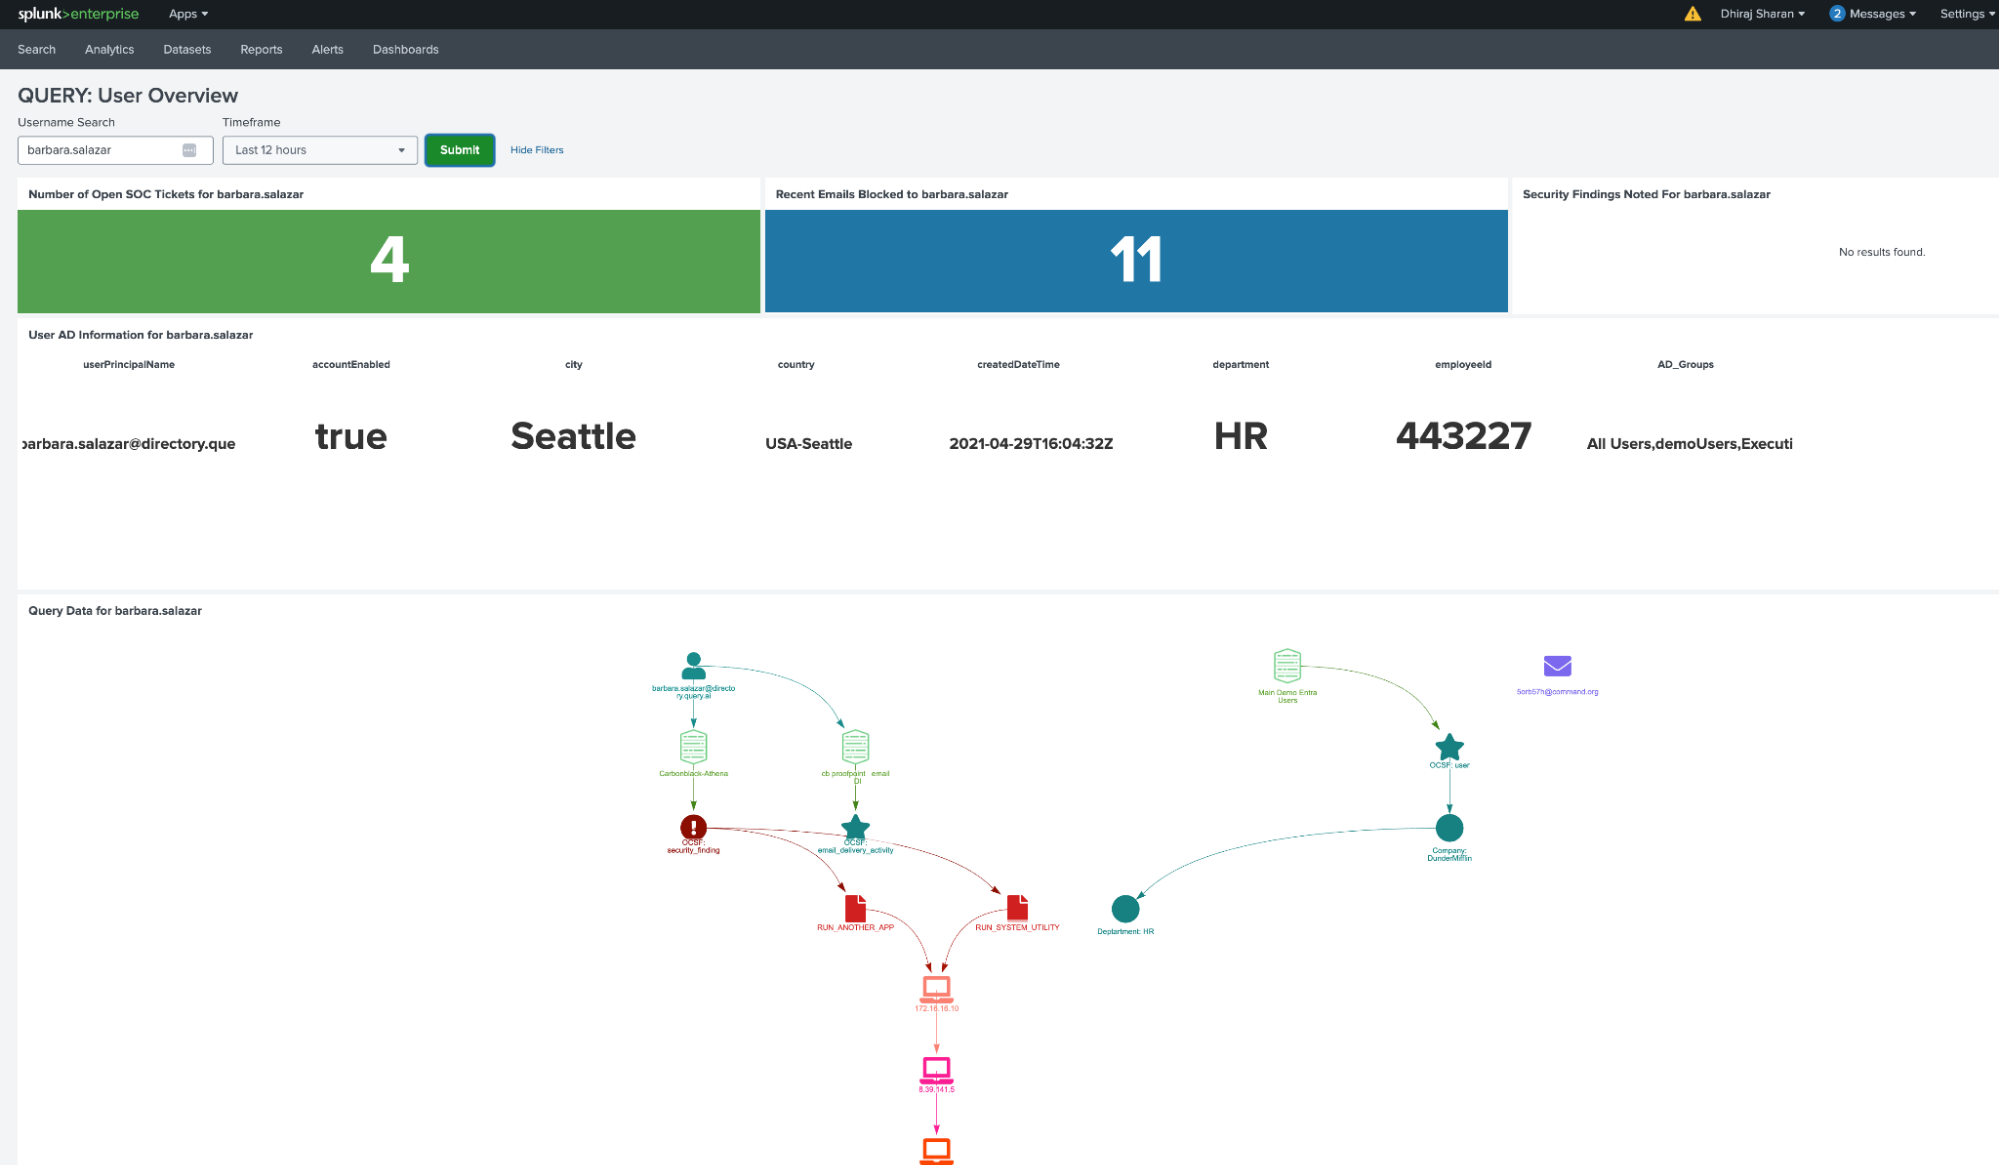
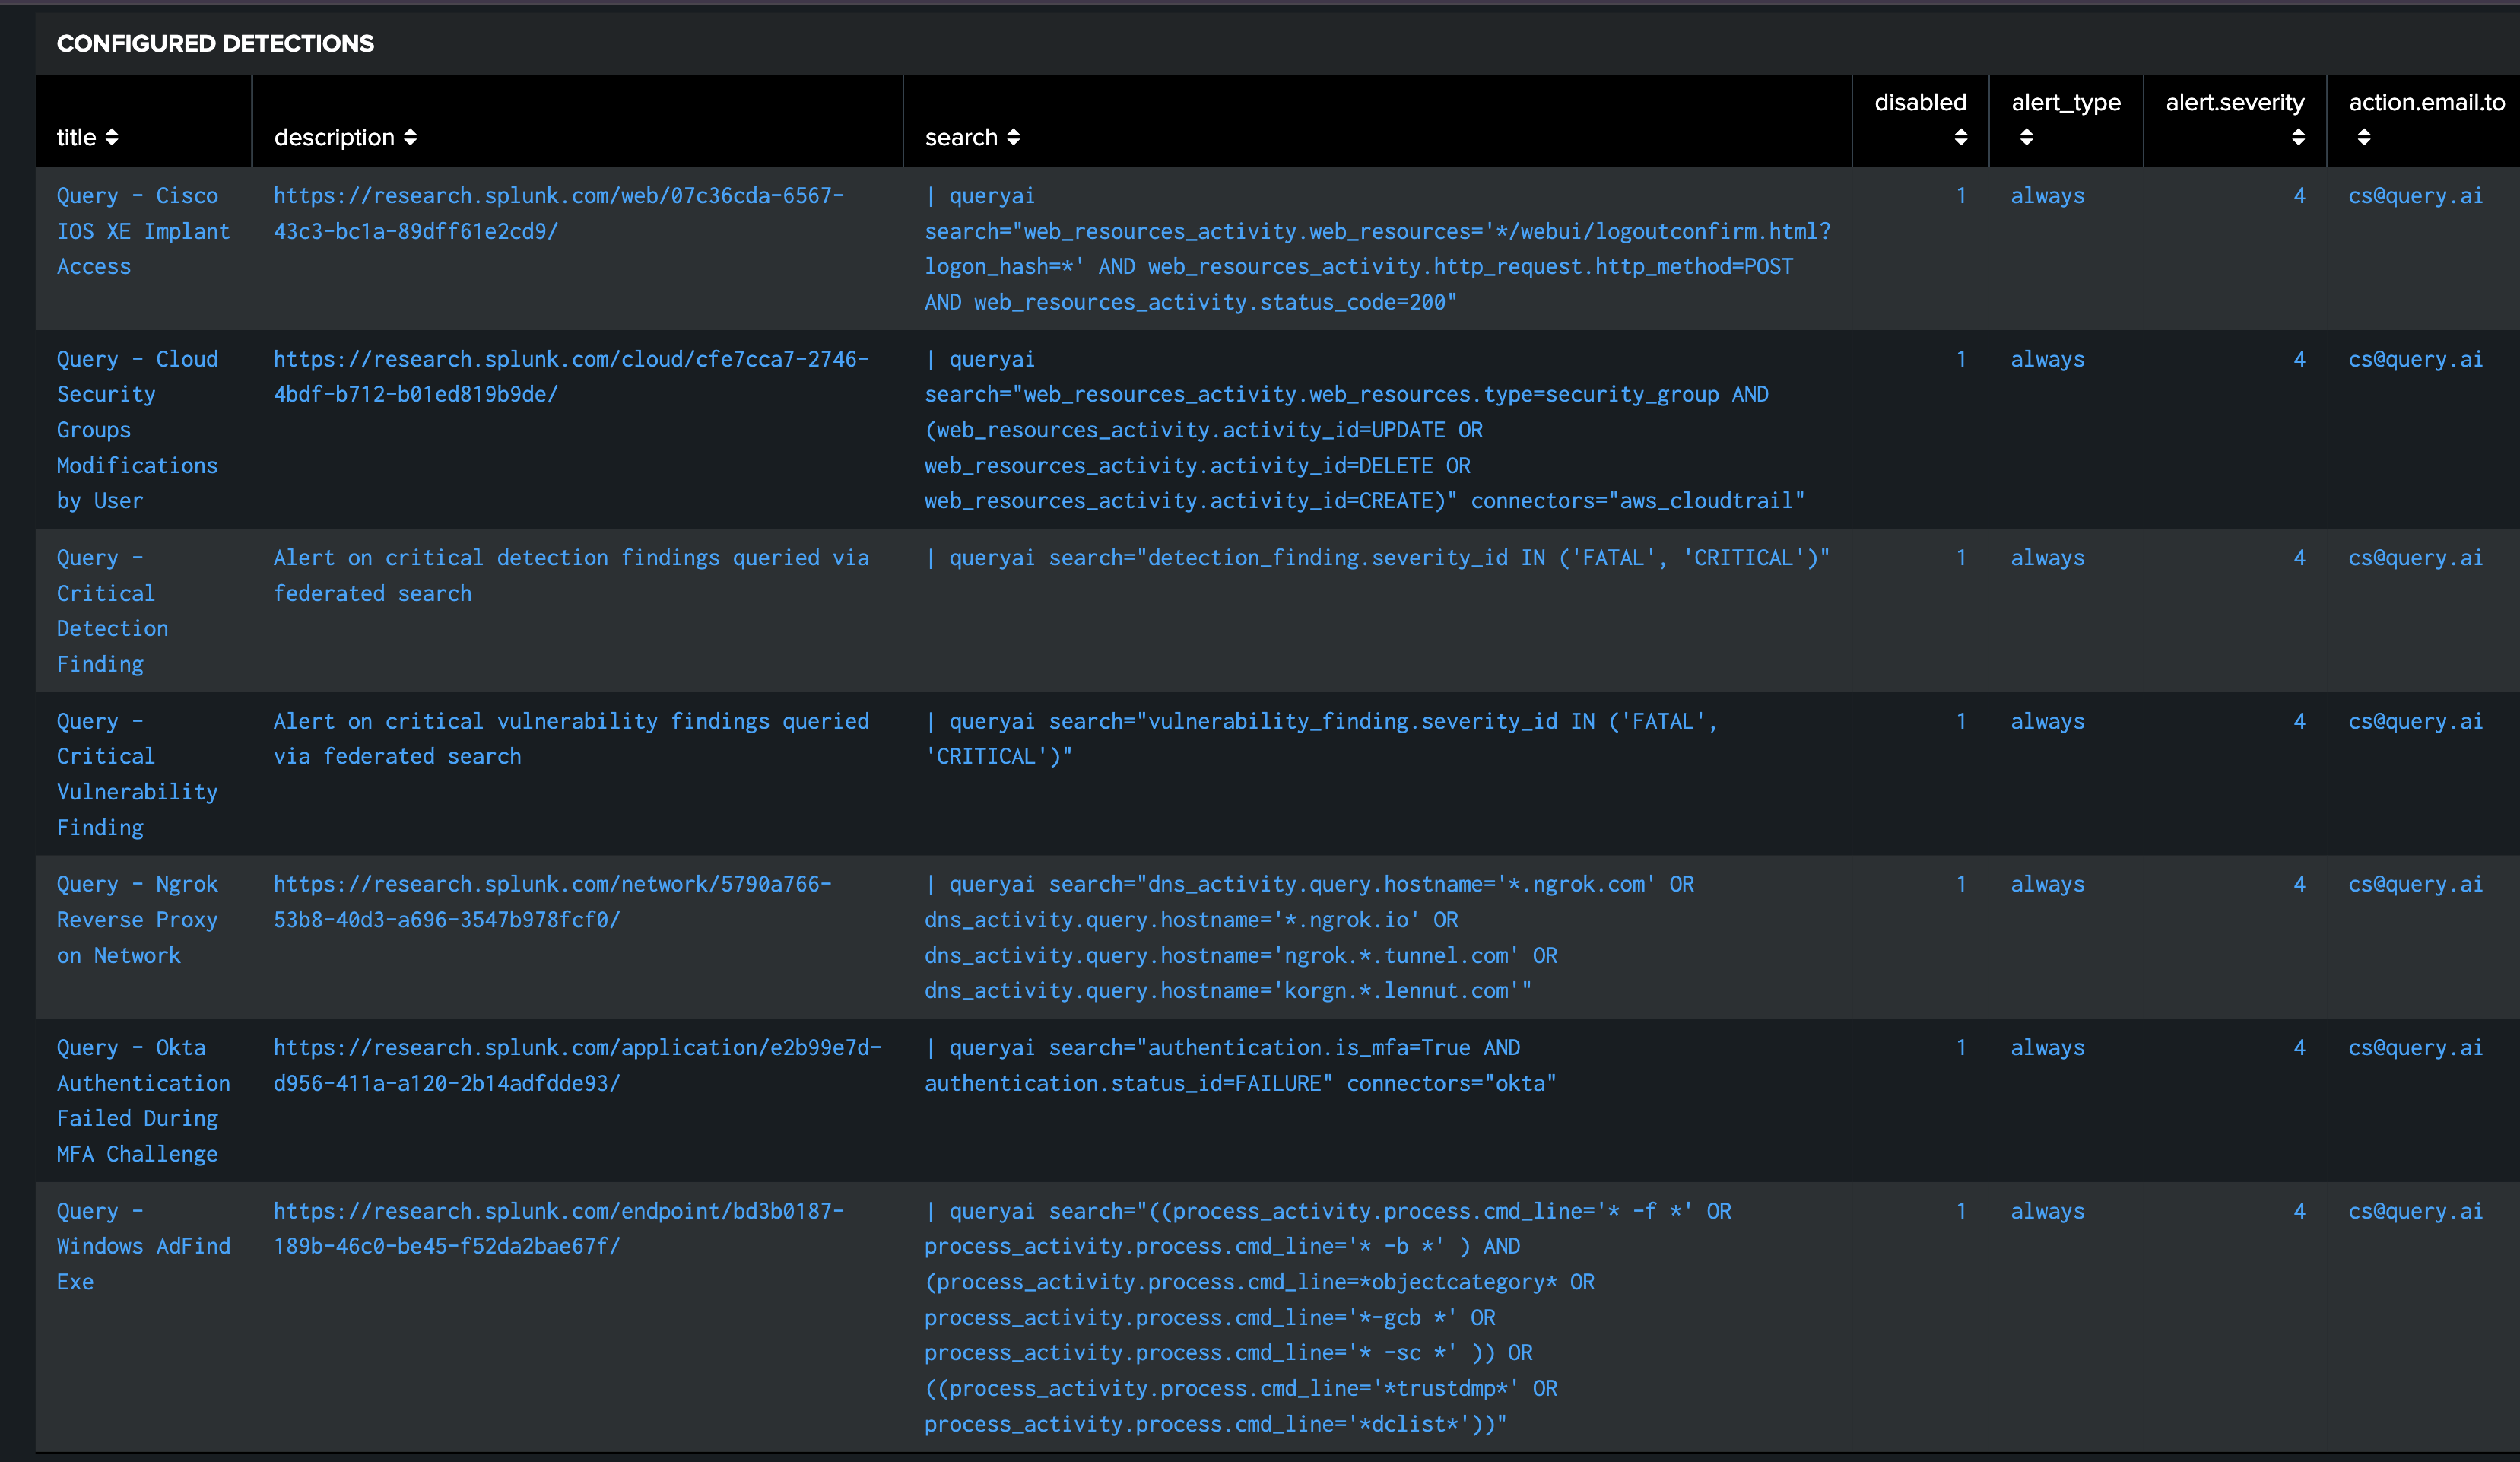
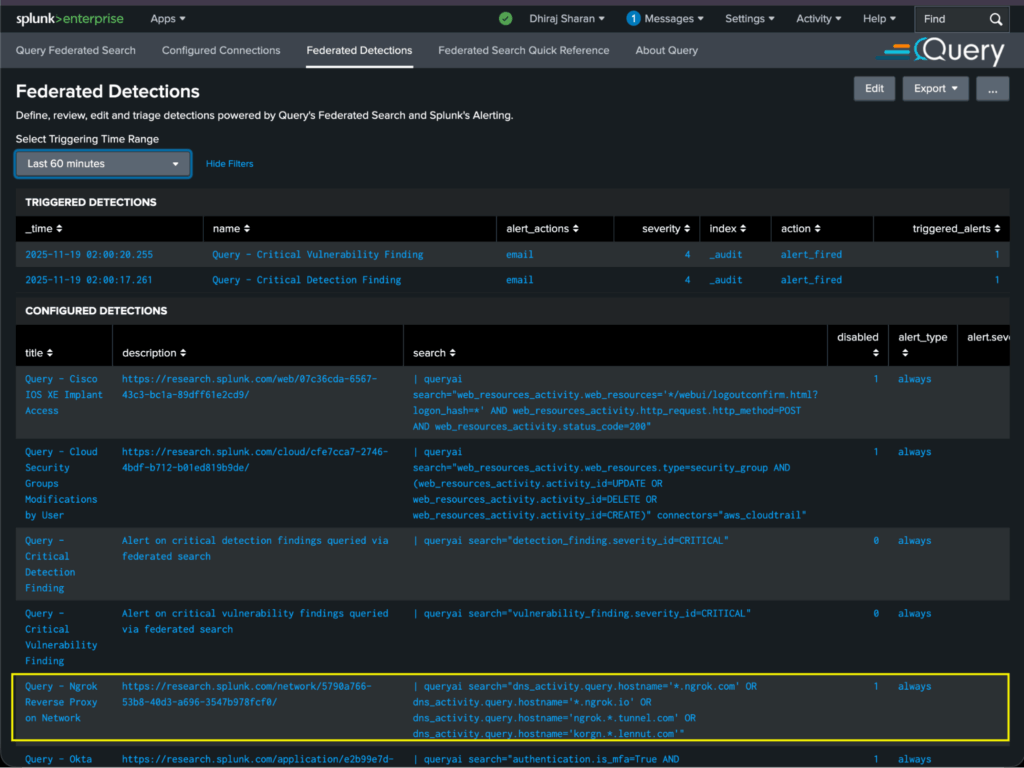
Query Federated Search for Splunk - Query
Announcing Query Splunk App 2.5 - Query
Splunk Format Command – Splunk Query – TEPEHL
Bucket In Splunk Query at Raymond Workman blog
Splunk SPL2 and BOTS - intro - YouTube
Product Release: Announcing Query Splunk App 3.0 - Query
Splunk Query Escape Quotes
Splunk Cheat Sheet: Search and Query Commands
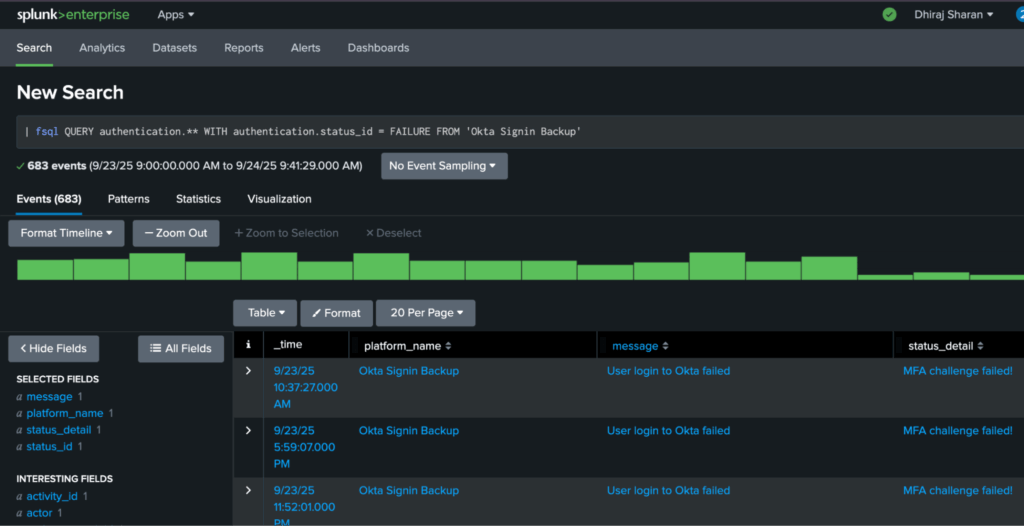
Getting Started with Query Federated Search for Splunk - Query
Using the SPL2 Module Editor for Incident Response... - Splunk Community
Splunk Query Example , Splunk Quick Reference Guide – OEJBAQ
AI Query Assistant for Splunk | Splunkbase
Query App for Splunk
Announcing Query Splunk App 2.4 - Query
Query Your Hydrolix Data in Splunk With SPL - Hydrolix
Splunk query editor | Grafana Enterprise Plugins documentation
Splunk Index Size Query at Karan Katz blog
Splunk Introduces SPL2 for Enhanced Search and Data Prep | QuantaSi ...
SPL query to find out the indexes created from the console (UI) | Splunk
Splunk Query Language Cheat Sheet – GGWE
Customer Success Story: How One Enterprise Used Query to Connect Splunk ...
Splunk Query In List – How to list all the KV stores /collections via ...
Splunk Query Builder Expert - Skill | Spark
If Condition In Splunk Query _ Splunk Cheat Sheet: Query, SPL, RegEx ...
Splunk Query Language and Data Analysis | Coursera
Splunk base query dashboard - creatorasse
What Query Language Does Splunk Use at Monte Rodriquez blog
Welcome to the Future of Data Search & Exploration | Splunk
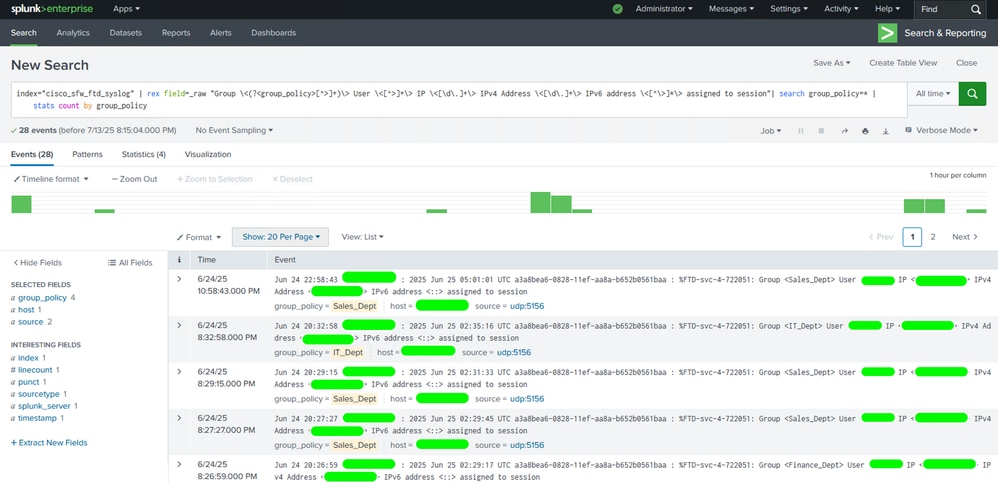
إنشاء لوحات معلومات وتنبيهات مخصصة على Splunk باستخدام Syslogs من FTD ...
How to use a lookup table in a splunk query? – lookup table matching – PBFF
How to use Splunk SPL commands to write better queries - Part I
Two Useful Settings to Improve Splunk Search Interface ...
Getting Started with SPL (Search Processing Language) in Splunk | by ...
Splunk Search Field Like | Splunk Spl Cheat Sheet – NQFLWV
Basic Searching in Splunk Enterprise - YouTube
Query on LinkedIn: #querysecdatachallenge #splunk #splunkbase #soc # ...
Customer Success Story: How this enterprise used Splunk to investigate ...
23 Top Splunk Queries for Threat Hunting You Needs Right Now
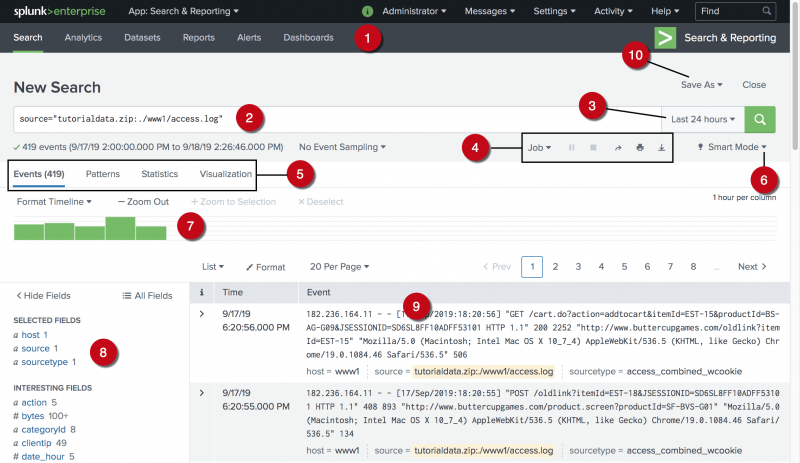
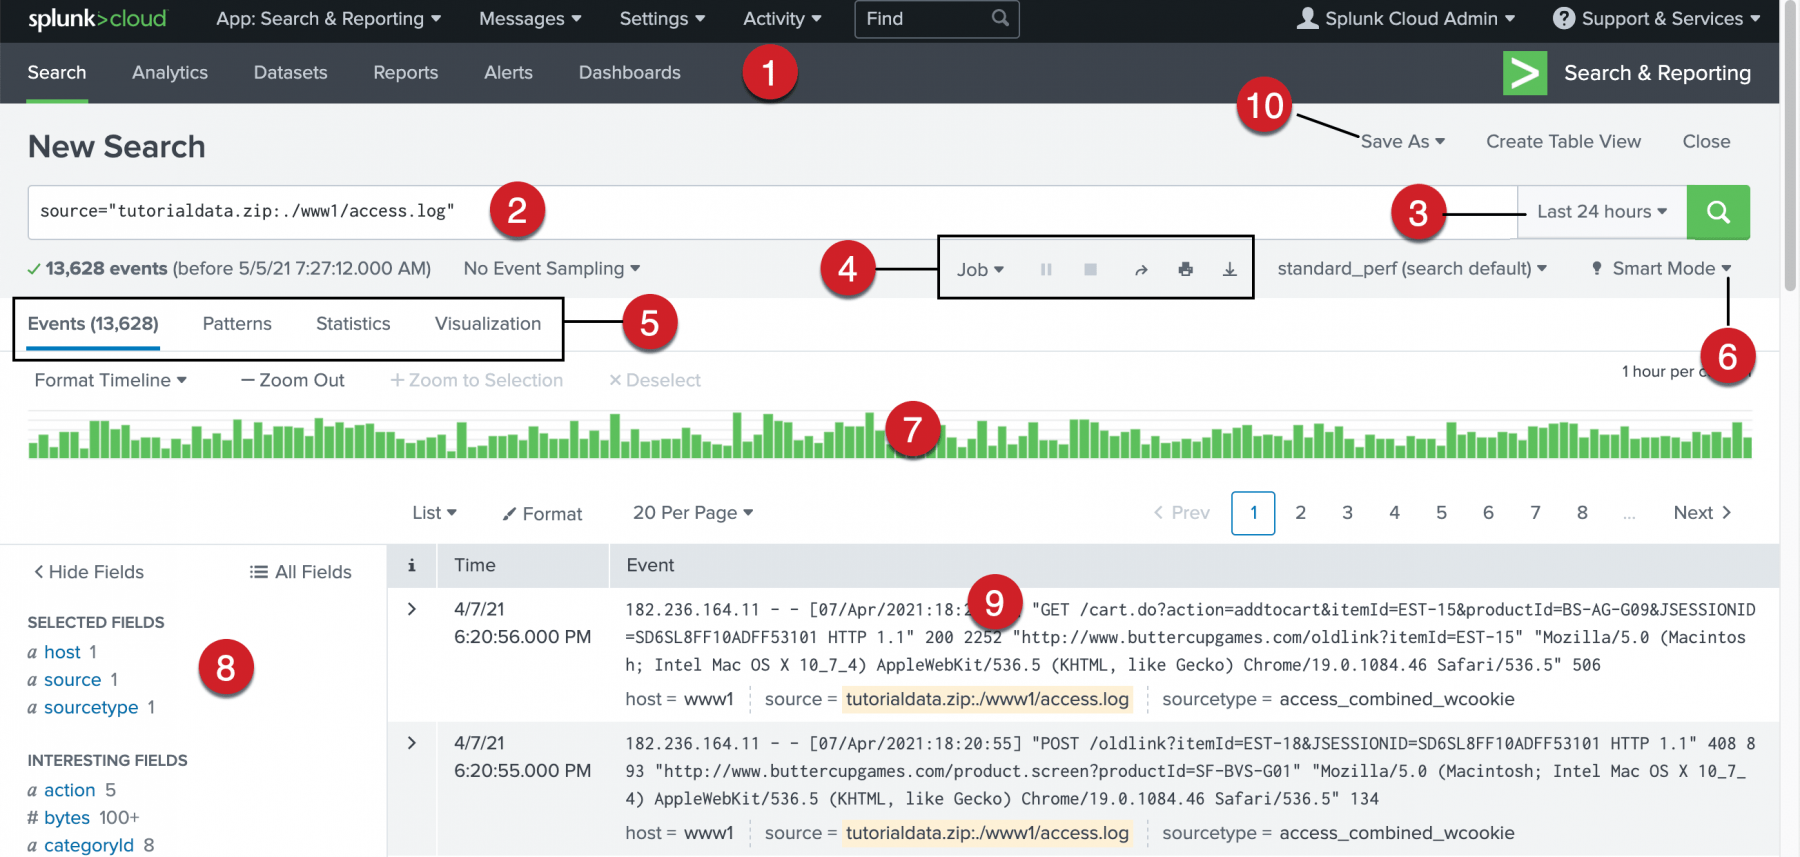
Exploring the Search views - Splunk Documentation
Splunk Use Cases | Splunk
Splunk Cheat Sheet - Query, SPL, RegEx, & Commands - Splunk | PDF | Tag ...
splunk search文 | splunk 使用方法 – ZRAVBE
Splunk Where Example at Tawana Tibbs blog
Create Custom Dashboards and Alerts on Splunk using Syslogs from FTD ...
Splunk SPL Queries for SOC Analysts: 50+ Essential Queries - Studocu
Splunk 搜索语言详解与使用示例 | Splunk 教程
Customer Success Story: How One Enterprise Connected Splunk and ...
15 Best Splunk Queries For SOC Analysts: From Novice To Pro
17. Intrusion Detection With Splunk (Real-world Scenario) | Exploit ...
Splunk Queries Pdf | Basic Splunk Search – EXJCD
How to skip pivots and get data faster | Query posted on the topic ...
Hunting the Suspicious Network Activity at GovWare 2025 Using Splunk
Splunk search basics (with real-life examples) – I-Space Research Labs
Threat Matching SPL query is missing for all sources in Threat ...
Mastering Search Queries in Splunk - Expertrec
Splunk The Basics | Kareem Ayman
Master Splunk SPL: Data Model Queries Explained with SQL-like Syntax ...
Splunk Custom Search Command: Searching for MISP IOC's - /dev/random
Splunk Fields Explained at Barbara Fowler blog
Refine your search with filters | Splunk Enterprise, Splunk Cloud ...
Splunk: How to Write a Query to Monitor Multiple Sources and Send Alert ...
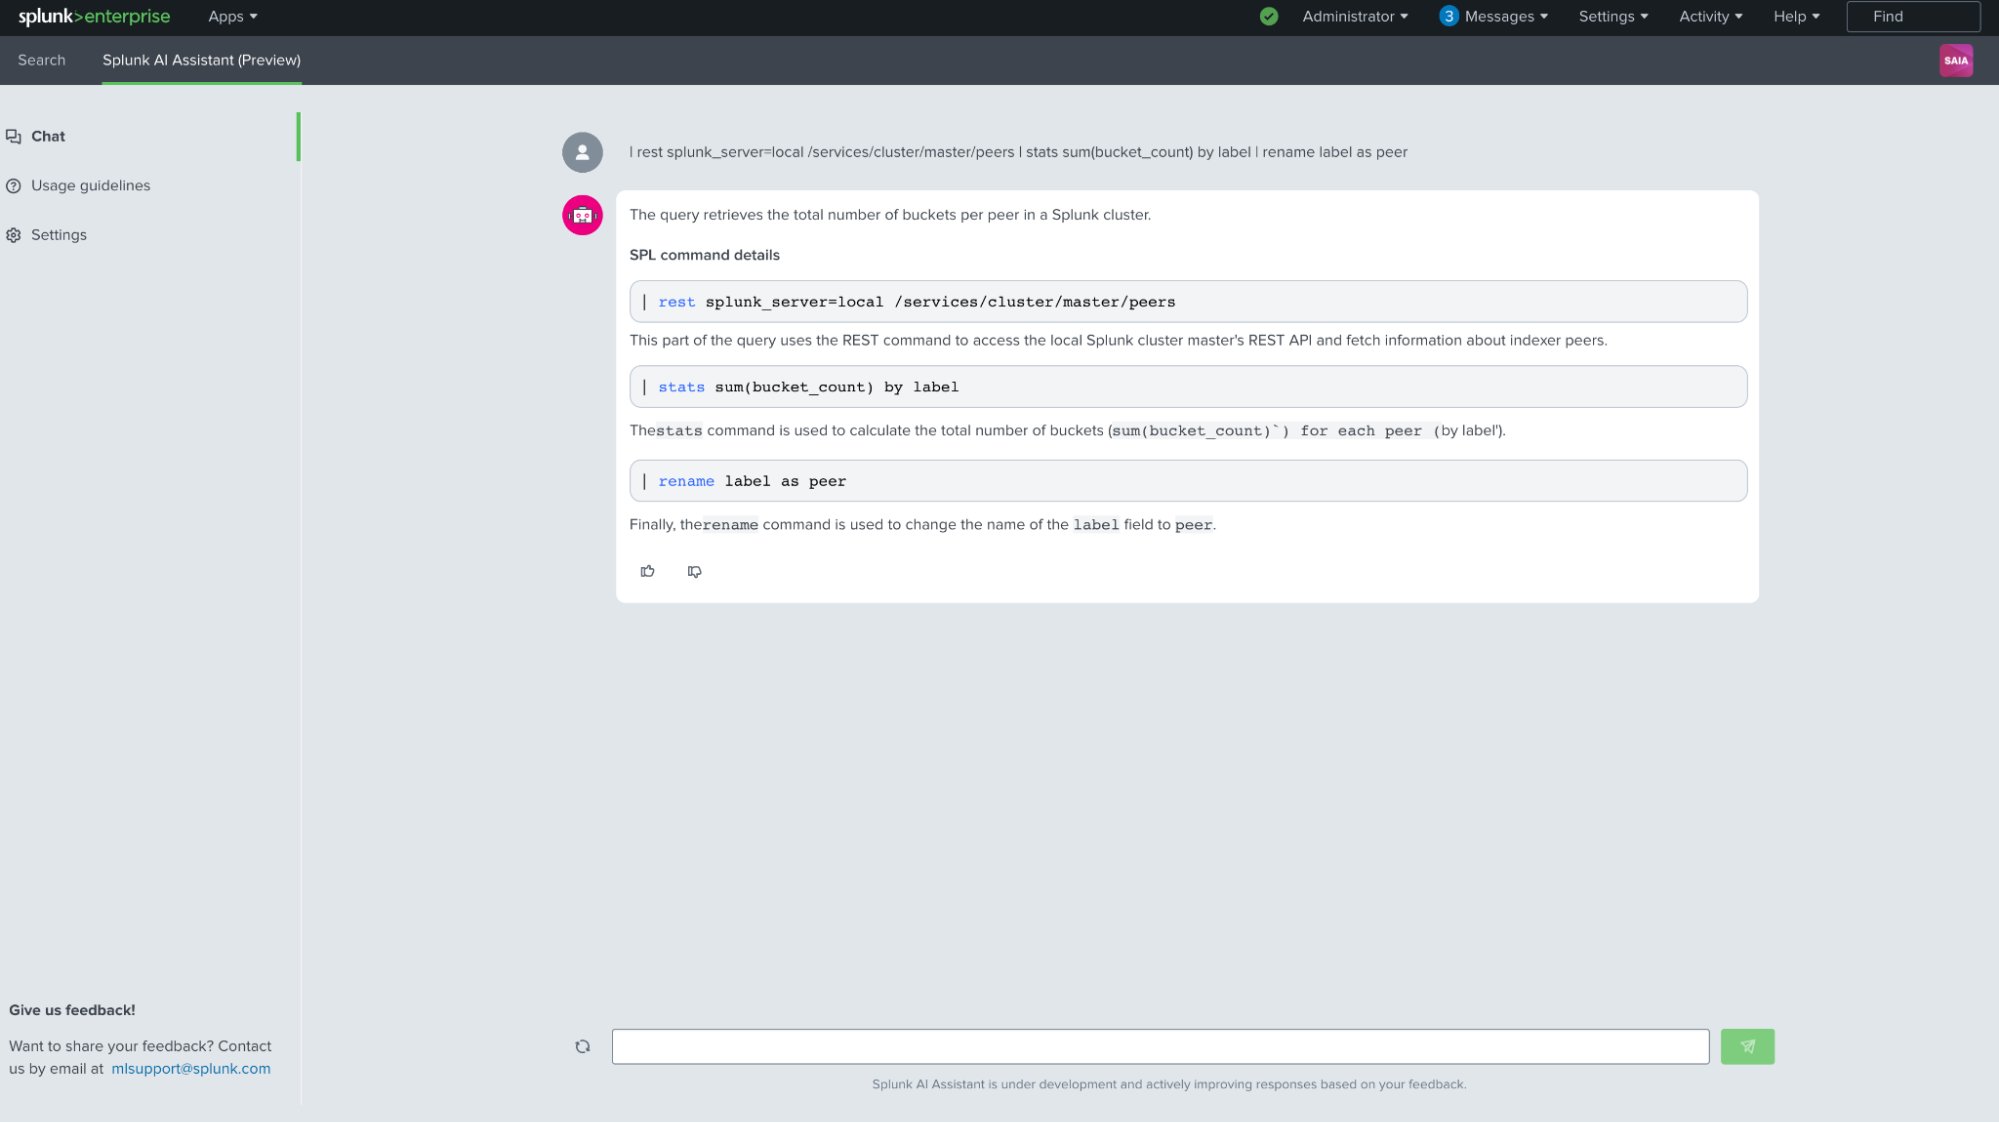
Simplifying SPL: A Beginner's Guide to the Splunk AI Assistant ...
Splunk SIEM: Search Processing Language (SPL) Basics – NetwerkLABS
Introducing Edge Processor for Splunk Enterprise: Data Management on ...
A Guide To Easy Log Analysis Using Splunk
Splunk Remote Upgrader for Linux Universal Forwarders | Splunk
Getting Started with Splunk Cloud Platform 2026 — Step-by-Step Beginner ...
Splunk Fieldformat Example at Crystal Yazzie blog
Splunk SPL Cheat Sheet 2026: Threat Hunting Queries
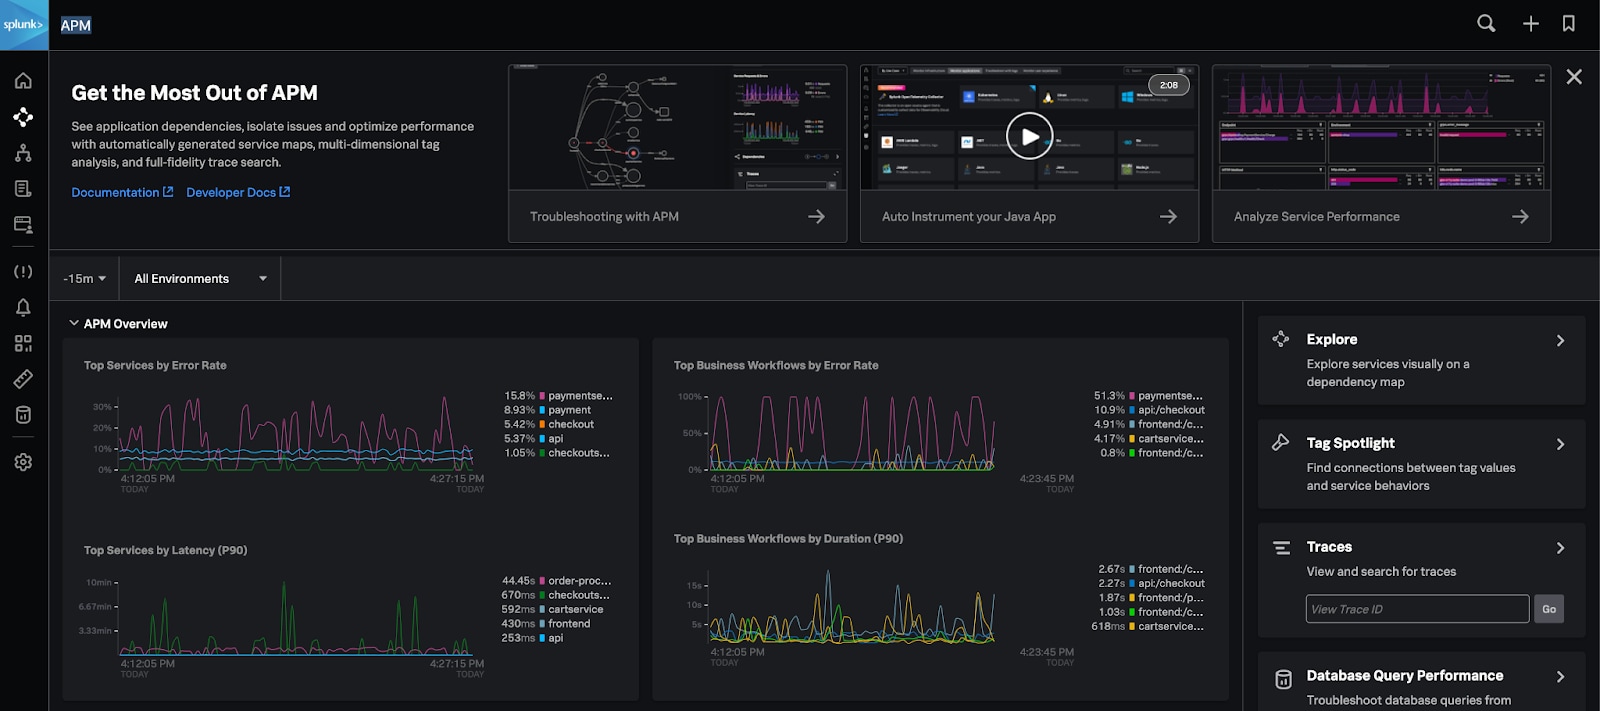
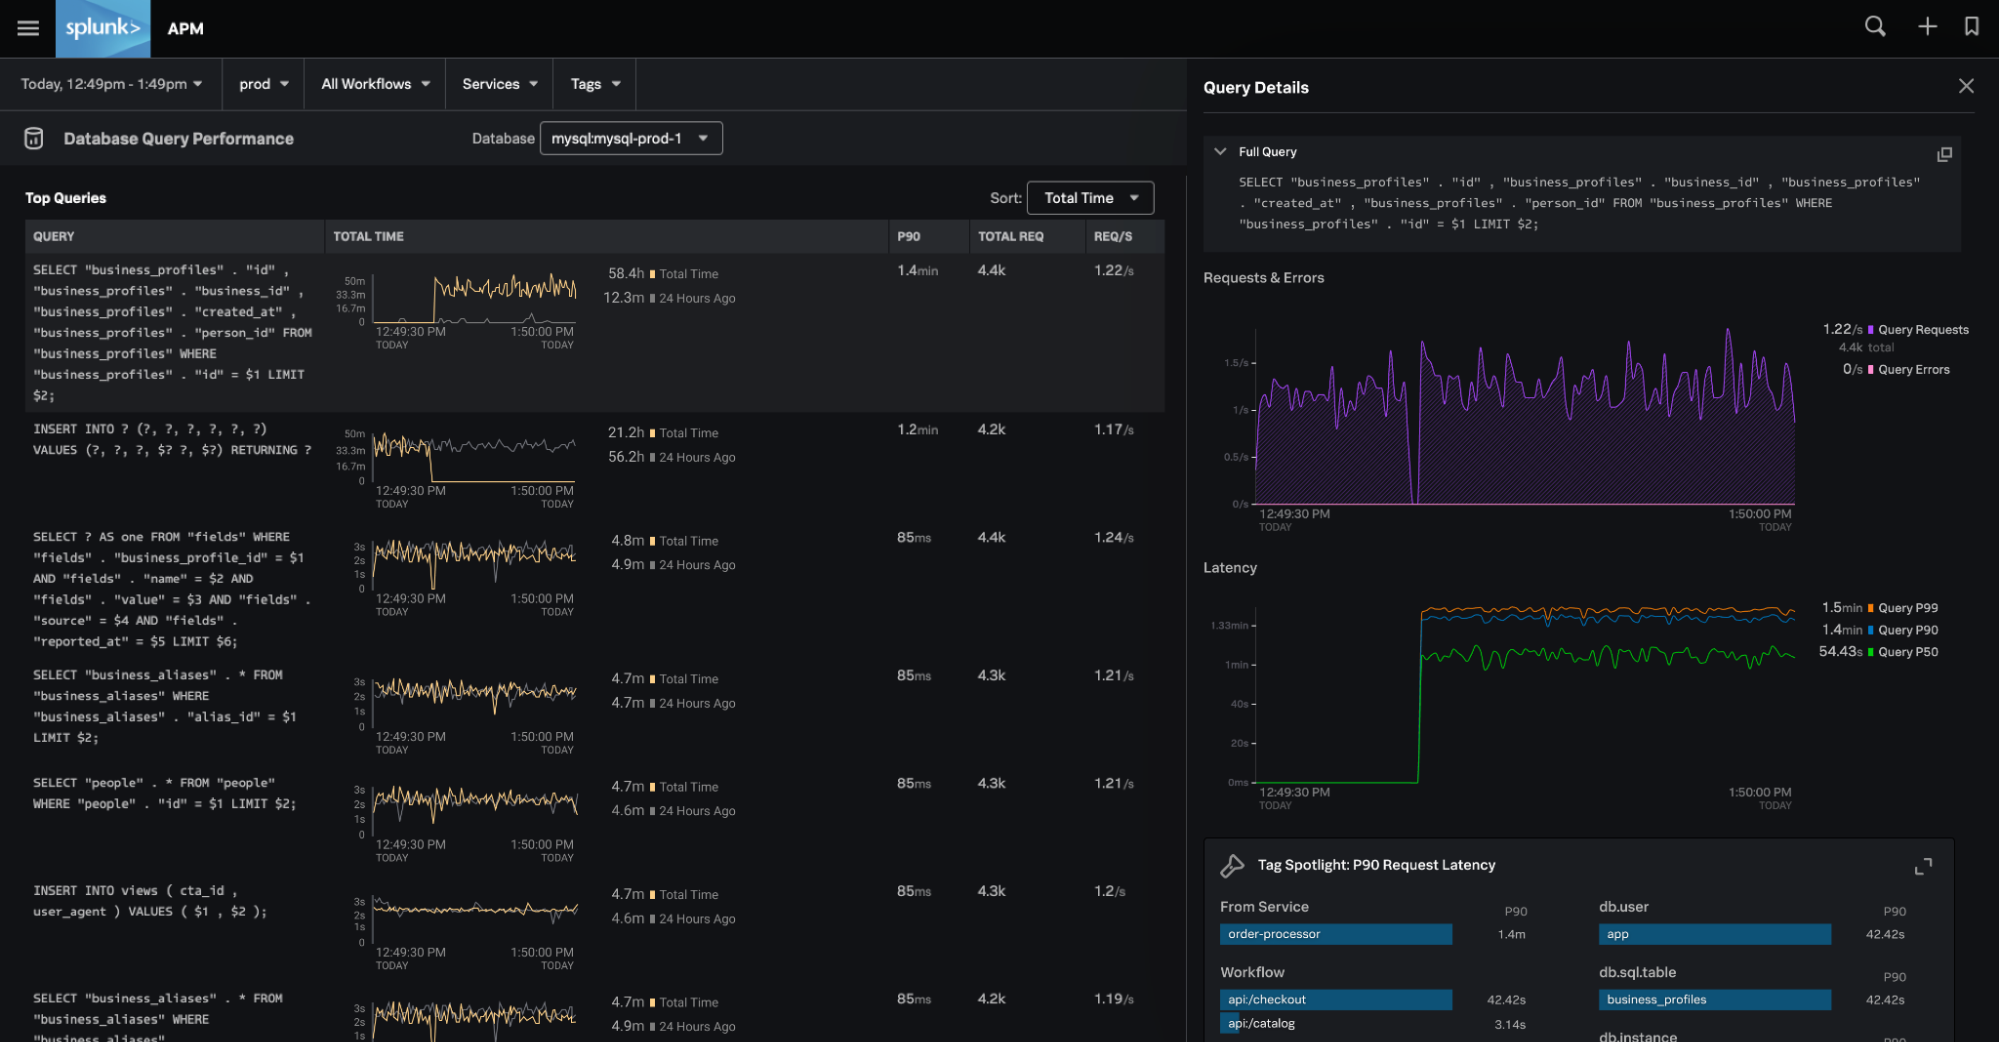
New: Optimize Slow Queries with Enhanced Database Visibility in Splunk ...
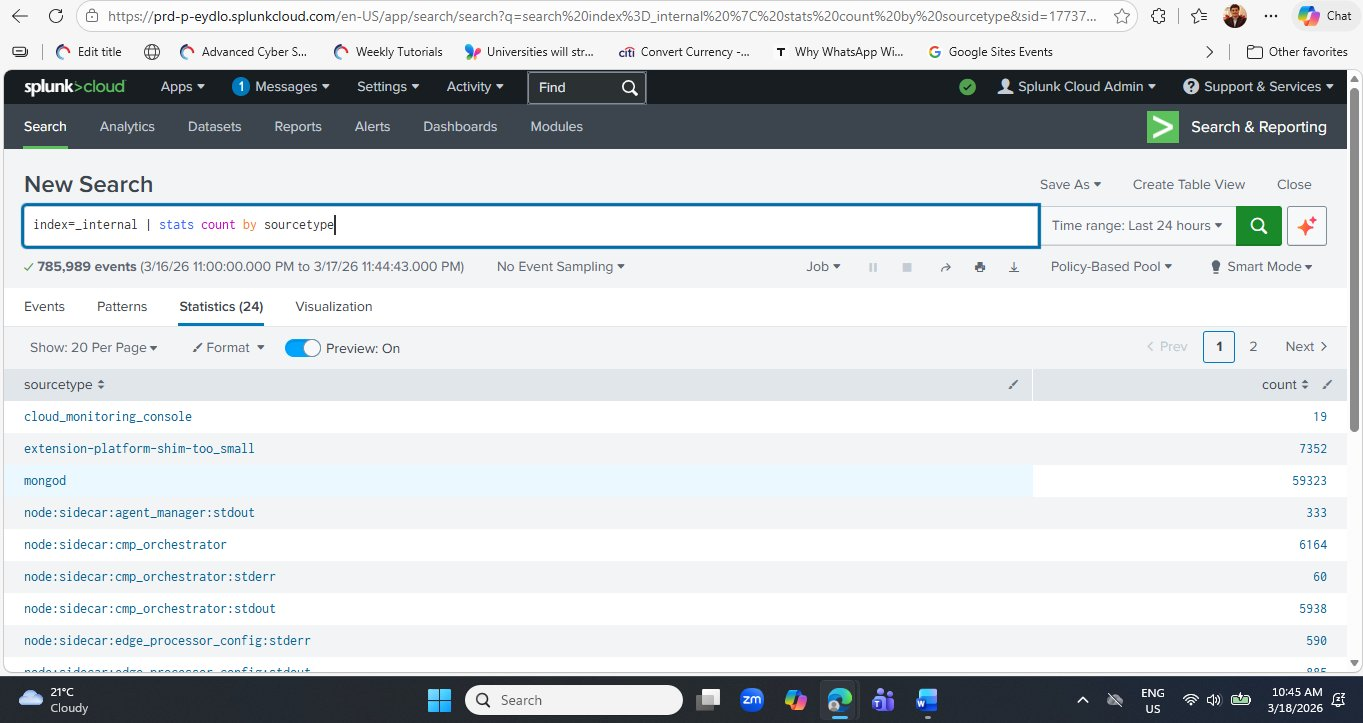
Part 2: A Beginner’s Guide to Basic Splunk Search and Navigation ...
Splunk PNW User Group - Seattle - 2023-06-28.pdf
Splunk - SquaredUp
Splunk 2 | CYB3RM3
Customer Success Story: How This Enterprise Is Transitioning From ...
Andrew Jarombek
Best Log Analysis Tools & Software in 2026 | SigNoz
Platform: Our Comprehensive Guide to SPL2: Navigating New Features and ...
TryHackMe | Splunk: Exploring SPL
Getting Started With Splunk: Basic Searching & Data Viz — Stratosphere IPS
Investigating With Splunk: WALKTHROUGH – A Cyber Journey
Say hello to SPL2, Splunk's next-generation data search and processing ...
Tech Talk | Boost Productivity with SPL2: The Next-Gen Language for ...
Splunk: Exploring SPL | FaresMorcy
Medium